Know what your SOC 2 report says before your customers read it.
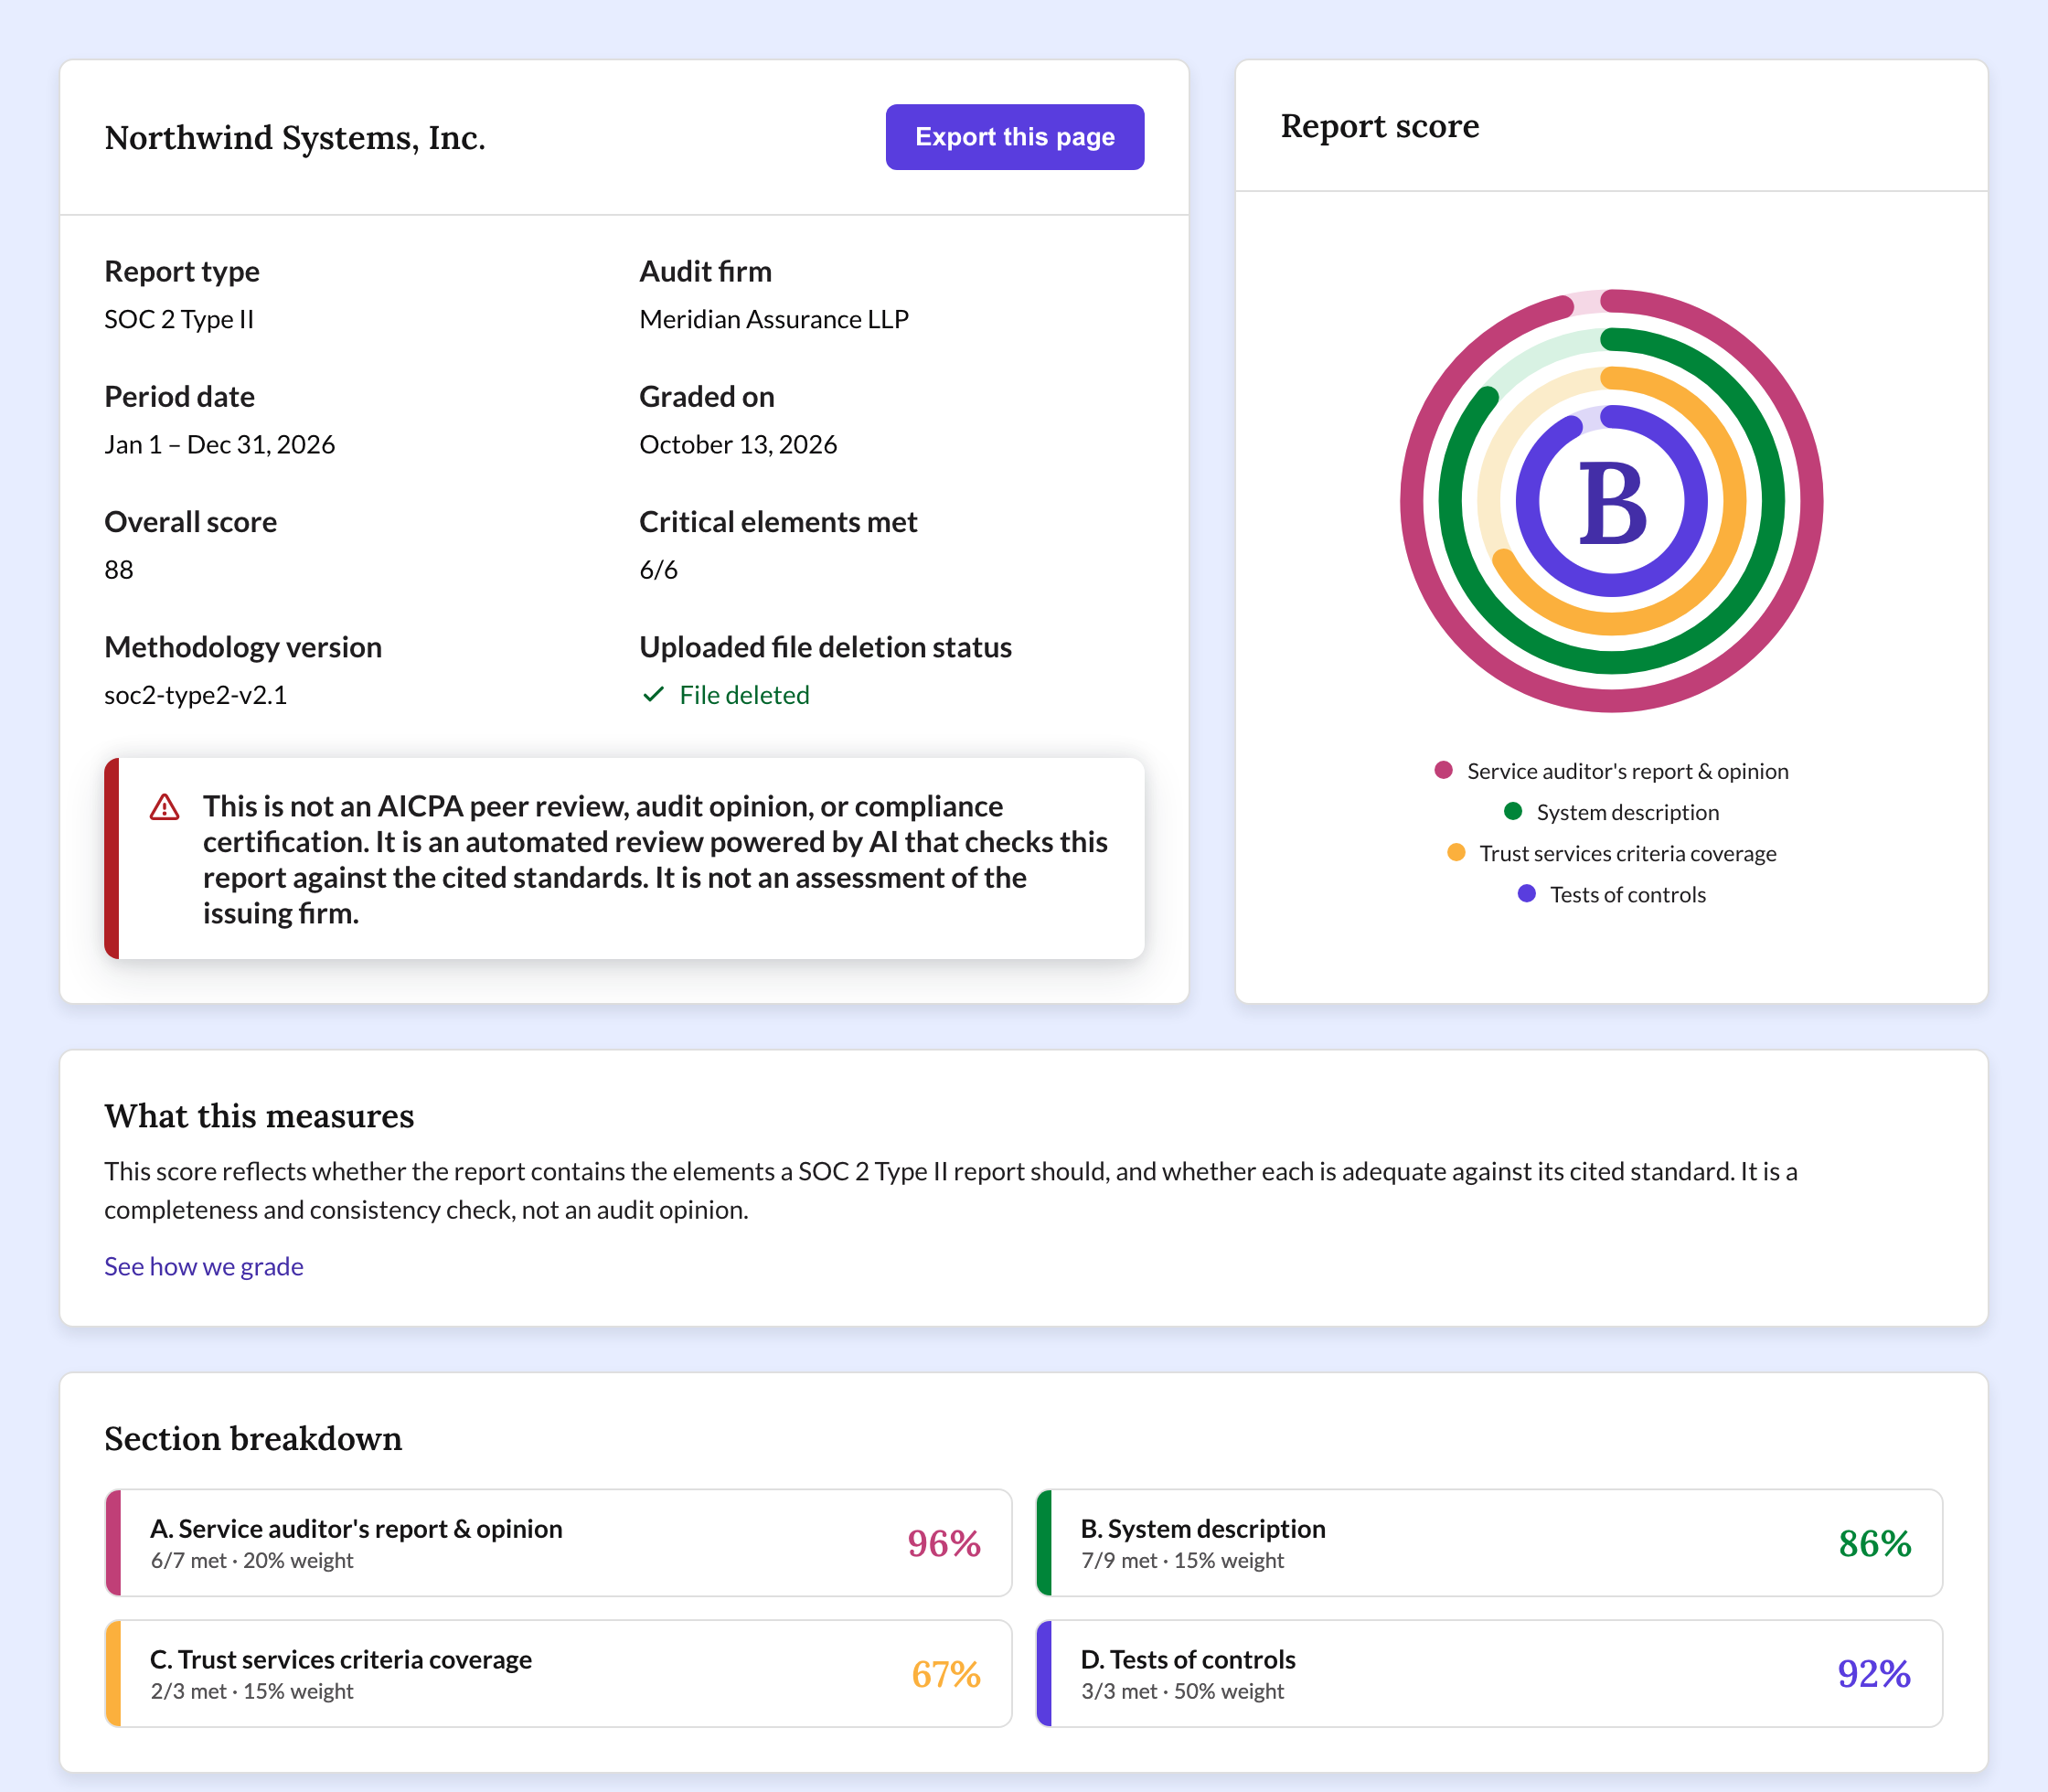
The Audit Report Grader checks your issued SOC 2 Type II report against the standards your auditor reports under and gives you a cited read on whether it’s complete and consistent. See where it’s thin before a customer’s security team asks.
Why run your own report
Your SOC 2 report gets read closely by every customer who asks for it. The grader shows you what they’ll find.
Customers’ security teams read the opinion, the system description and the test results. See whether each contains what the standards require.
Spot a system description or test results that read as boilerplate, with the cited standard next to each finding.
Take a cited list of findings to your audit firm. They issued the report and can explain how each element was handled.
What it checks
22 elements across four sections, each tied to the standards auditors report under. It checks whether your report contains what those standards require, not whether your controls are effective. The grader checks against the standards. It doesn’t set them.
What kind of opinion was issued, what it covers, the period, and management’s assertion.
Whether the description of your services, systems, commitments and vendors covers what DC 200 requires.
Whether the trust services categories in scope are named and every applicable criterion is addressed.
Whether each control’s test is described with specifics and its result is stated clearly.
The critical gate
The grader’s methodology treats six elements as critical, each tied to AT-C 205, DC 200, TSP 100 or the SOC 2 Guide. If any one is missing or inadequate, the grade is capped at F regardless of the numeric score.
How it works
- 1Upload an issued report
A SOC 2 Type II report you’re authorized to share. PDF, up to 20 MB.
- 2AI classifies each element
A model running in our own cloud account reads the report at temperature zero, marks each of the 22 elements and quotes the supporting text.
- 3Code computes the grade
The score runs in code, never in the model, so every report is scored by the same math.
How we handle your report
An issued SOC 2 report is confidential. Here’s how the grader handles yours.
An AI model running in Audora’s own cloud account reads the report at temperature zero. It classifies and quotes; code computes the score.
Modern TLS in transit, and encryption at rest with automatically rotated keys.
Score summaries may be included in aggregated statistics that never identify you or your firm.
We don’t sell your report or your personal data. Contact details you provide follow our privacy policy.
Common questions
Is this an assessment of our auditor?
No. It reads what the report contains and checks it against the cited standards. It isn’t an AICPA peer review, an audit opinion or an assessment of the issuing firm. Questions about a finding are best taken to your audit firm, which issued the report.
Read the methodologyDoes a good grade mean we’re secure?
No. The grader reads the report, not the controls behind it. A complete, consistent report can still disclose exceptions; the grade tells you whether the report states them clearly.
Read the methodologyWho sees our grade?
Only the person who uploaded the report. We don’t publish grades or scorecards.
Grade a free reportWhat happens to our report?
An AI model in Audora’s own cloud account reads it, it’s encrypted in transit and at rest, and it’s used to produce your grade. Your score summary may be included in aggregated statistics that never identify you or your firm. For retention details, email security@goaudora.com.
Security and trust at AudoraWhich reports can we upload?
Your issued SOC 2 Type II report, as a PDF up to 20 MB, that you’re authorized to share. Type 1 reports, drafts and SOC 1 reports aren’t graded.
Grade a free report
The Audit Report Grader is not an AICPA peer review, audit opinion or compliance certification. It is an automated review powered by AI that checks a report against the cited standards. It is not an assessment of the issuing firm.