Grade your SOC 2 Type II report.
The Audit Report Grader checks an issued SOC 2 Type II report against the authoritative standards and gives you a cited read on whether it’s complete and consistent — for the firm that wrote it and the company that holds it. See where it falls short before anyone else reads it.
Are you an auditor?
Peer-review-ready reports that hold up to anyone reading them.
- Check an issued report against AT-C 205, DC 200 and the SOC 2 Guide, element by element
- Compare reports across engagement teams
- Set a baseline before your next reporting cycle
Do you hold a SOC 2 report?
Know what your report contains before your customers read it.
- See whether it includes what the standards require
- Find where the system description or test results are thin
- Read every finding next to the standard it cites
What it checks
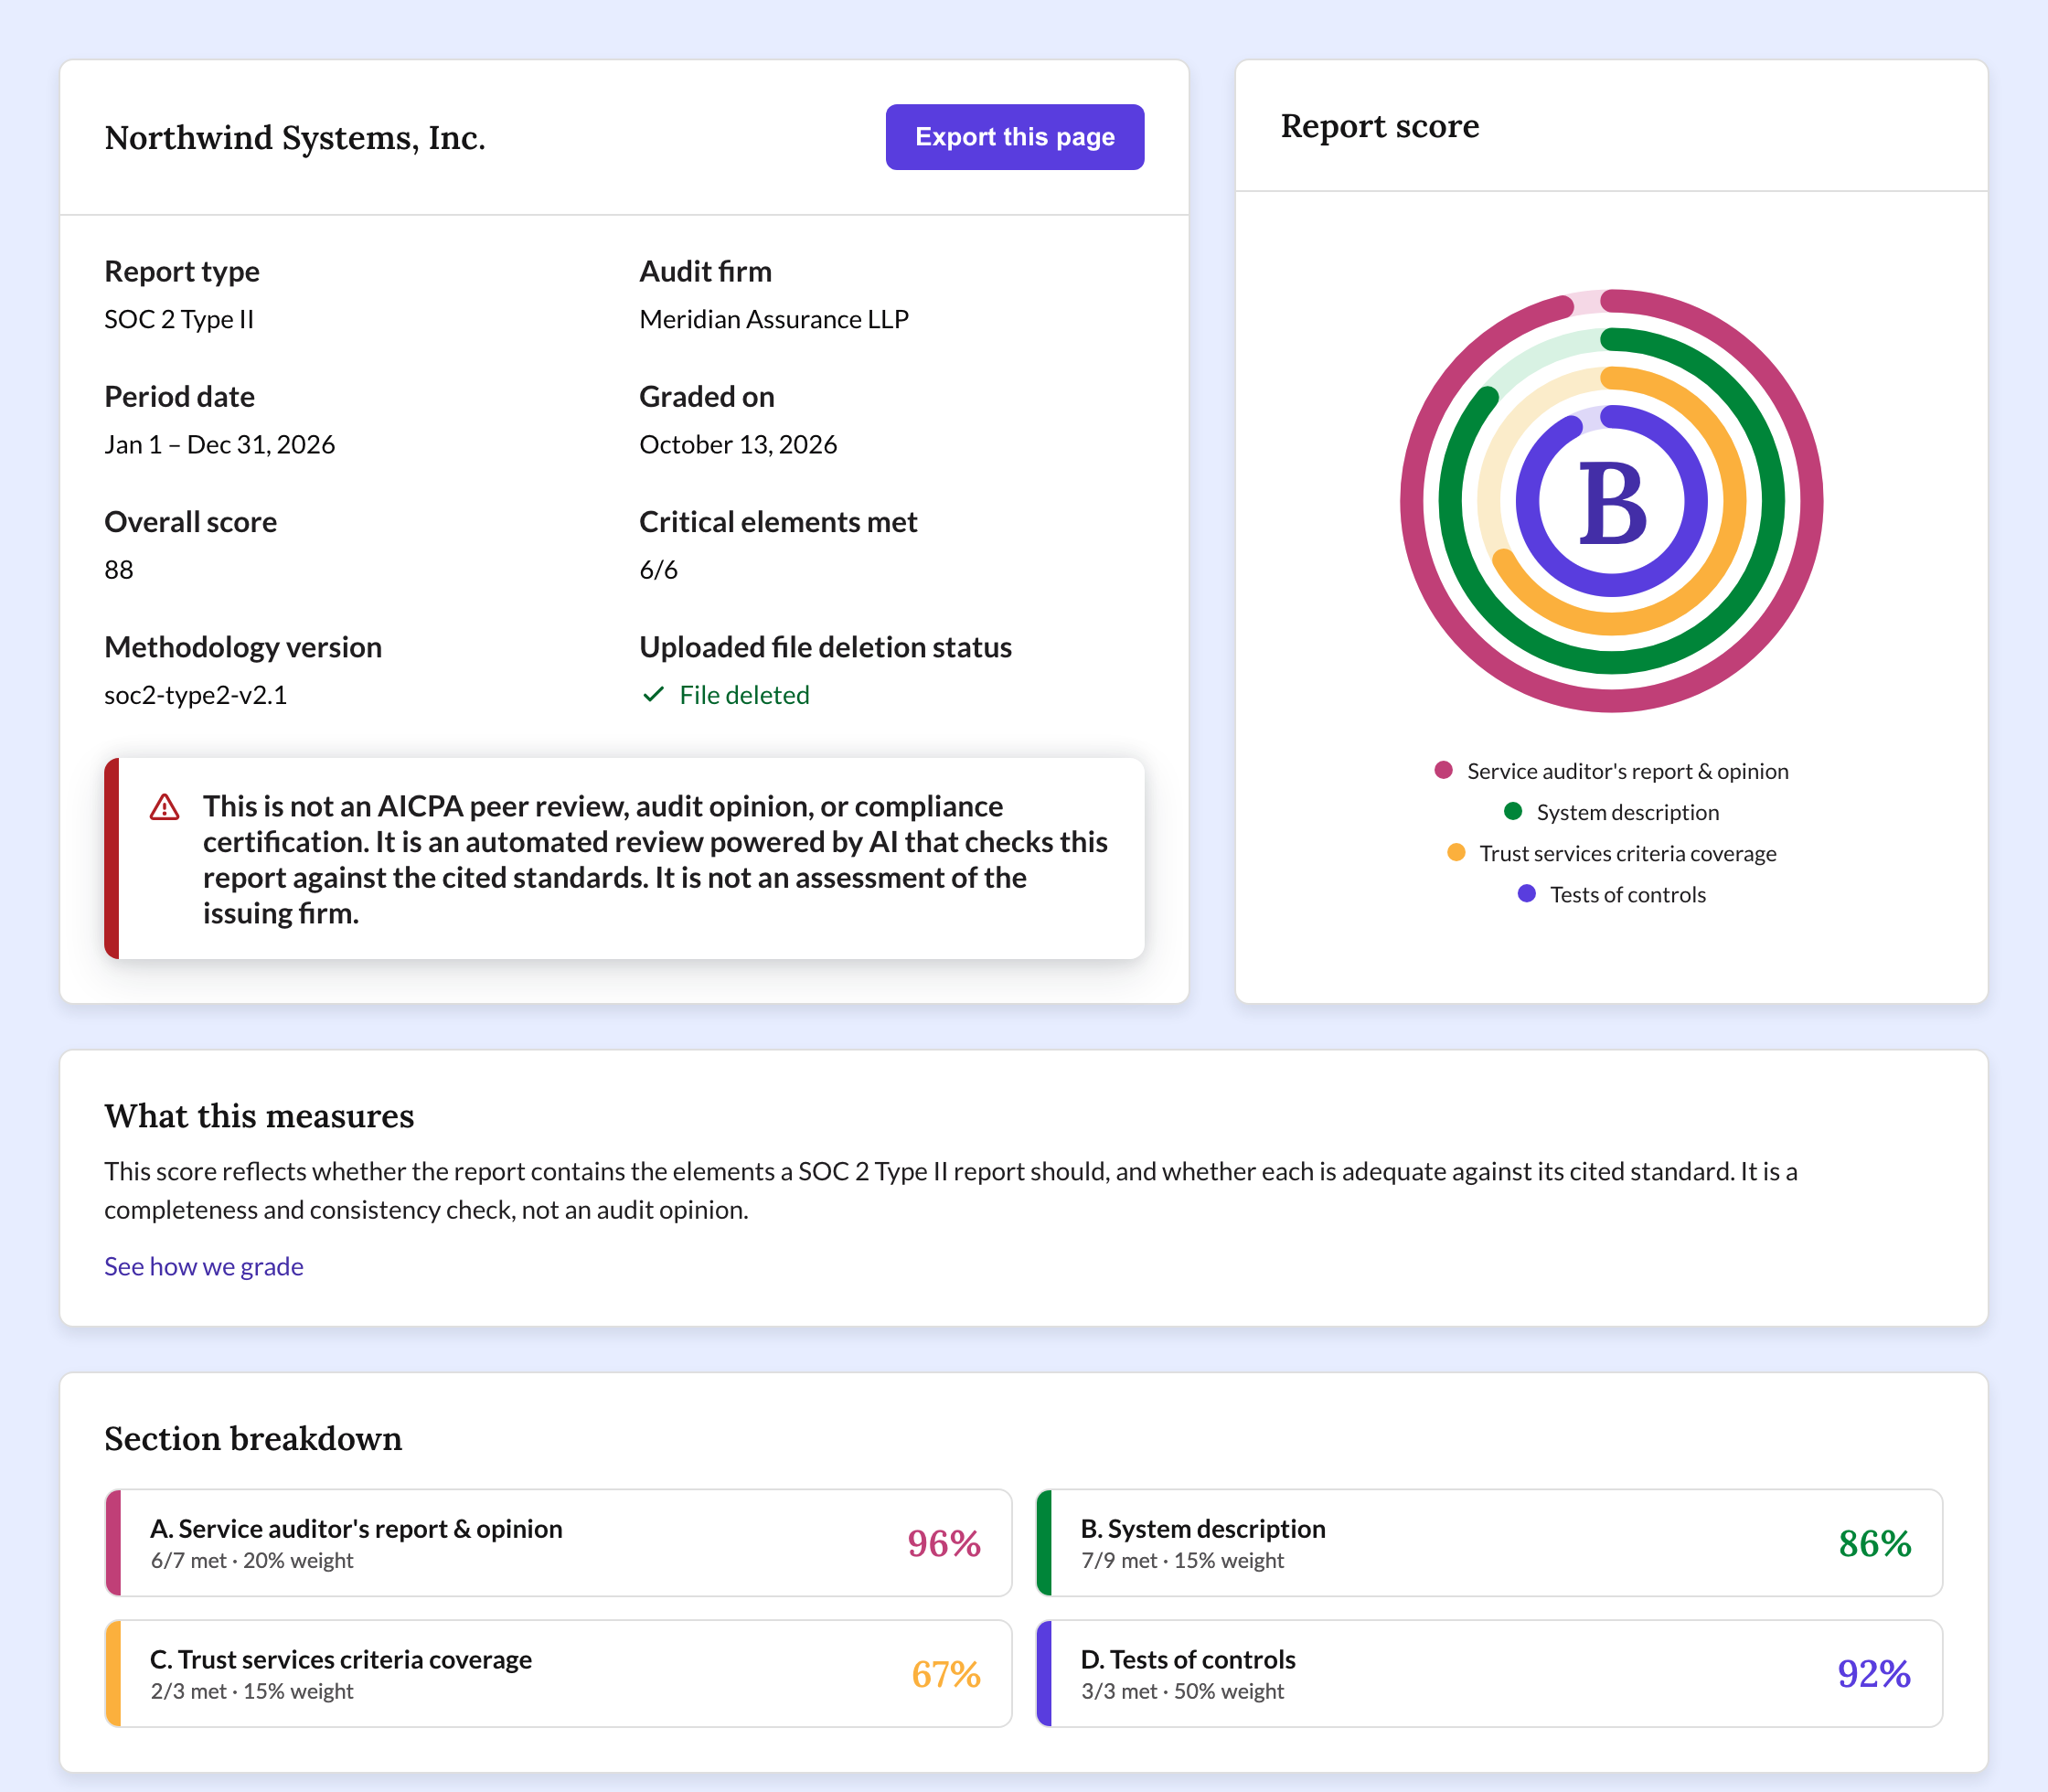
22 elements across four sections, each tied to an authoritative source. It checks whether the report contains what the standards require — not whether the underlying controls are effective. The grader checks against the standards. It doesn’t set them.
Opinion type, scope, management's assertion, restricted-use alert and auditor identification.
The nine description criteria in DC 200, from services and commitments to subservice organizations and changes.
In-scope categories named, every applicable criterion mapped and tested, exclusions explained.
Procedures described with specifics, results stated, and each control traced to a criterion, test and result.
The critical gate
The grader’s methodology treats six elements as critical, each tied to AT-C 205, DC 200, TSP 100 or the SOC 2 Guide. If any one is missing or inadequate, the grade is capped at F regardless of the numeric score.
How it works
- 1Upload an issued report
A SOC 2 Type II report you’re authorized to share. PDF, up to 25 MB.
- 2AI classifies each element
A model running in our own cloud account reads the report at temperature zero, marks each of the 22 elements and quotes the supporting text.
- 3Code computes the grade
The score runs in code, never in the model, so the same report gets the same grade every time.
How we handle your report
An issued SOC 2 report is confidential. Here’s how the grader handles yours.
An AI model running in Audora’s own cloud account reads the report at temperature zero. It classifies and quotes; code computes the score.
Modern TLS in transit, and encryption at rest with automatically rotated keys.
Score summaries may be included in aggregated statistics that never identify you or your firm.
We don’t sell your report or your personal data. Contact details you provide follow our privacy policy.
Common questions
Is this a peer review?
No. It’s an automated completeness and consistency check against the cited standards. It isn’t an AICPA peer review, an audit opinion or a certification, and it isn’t an assessment of the issuing firm.
Read the methodologyWhat happens to my report?
An AI model in Audora’s own cloud account reads it, it’s encrypted in transit and at rest, and it’s used to produce your grade. Your score summary may be included in aggregated statistics that never identify you or your firm. For retention details, email security@goaudora.com.
Security and trust at AudoraWhy was my report capped at F?
One of six critical elements was missing or inadequate: the opinion type, the opinion’s subjects, the scope and period, management’s assertion, the in-scope categories or the test results. Without any one of them, a core requirement of the report is missing or unreliable.
See the critical gateWhich reports can I upload?
Issued SOC 2 Type II reports, as a PDF up to 25 MB, that you’re authorized to share. Type 1 and SOC 1 reports aren’t graded.
Grade a free reportDoes a good grade mean the company is secure?
No. The grader reads the report, not the controls behind it. A complete, consistent report can still disclose exceptions — the grade tells you whether the report states them clearly.
Read the methodology